

Bengaluru-based security technology company SecureDApp on 2 November 2026 launched SecureCMS, a DPDP consent management platform for banks, non-banking financial companies (NBFCs) and other financial institutions. The platform records verified customer consent across every channel and syncs withdrawals to core banking systems ahead of India’s Digital Personal Data Protection (DPDP) Rules deadlines.
The launch comes days before the Consent Manager provisions of the DPDP Rules, 2025 take effect on 13 November 2026. The main notice, consent, security and breach-reporting duties follow on 13 May 2027, leaving lenders roughly six months to clean up how they capture and prove consent. Elets BFSI has tracked this shift in its analysis of DPDP and the AI reckoning in India’s BFSI sector.

What SecureCMS does for banks and NBFCs
SecureDApp said the product was designed around banking workflows rather than a website cookie banner. Its main features include:

- OTP-verified consent at branches, mobile and net banking, direct selling agents (DSAs), business correspondents, call centres and WhatsApp
- Purpose-level consent records for each product, with the notice version and language stored, in English and all 22 Eighth Schedule languages
- Real-time sync of consent withdrawals to core banking, loan origination, CRM and marketing systems through APIs, webhooks and SDKs
- A legal-hold engine that separates “stop processing” from “erase”, so retention rules under the Prevention of Money Laundering Act and RBI KYC norms are respected
- Data limits for DSAs and collection agencies, rights-request workflows and a tamper-evident audit trail for auditors or the Data Protection Board
Why DPDP consent is harder for lenders
Under Section 6 of the DPDP Act, consent must be free, specific, informed and limited to the data needed, and the burden of proving it sits with the business. A single “I agree” at onboarding covering marketing, cross-selling and partner sharing is unlikely to meet that bar. Many banks still hold consent as a simple yes or no flag in a CRM, with no record of which notice a customer saw or when.
NBFCs face an added layer through the RBI (Digital Lending) Directions, 2025, which require explicit, granular consent and audit trails. The company also noted that Account Aggregator consent covers only specific financial data requests and does not replace DPDP consent, a point relevant as Sahamati revises Account Aggregator pricing for lenders. Penalties under the Act run up to ₹250 crore for security failures that lead to a breach.

Data protection is already climbing bank board agendas, as seen when Canara Bank reportedly invested over ₹50 crore in DPDPA compliance, and as the regulator tightens cyber checks on banks and NBFC APIs.
What SecureDApp’s leaders said
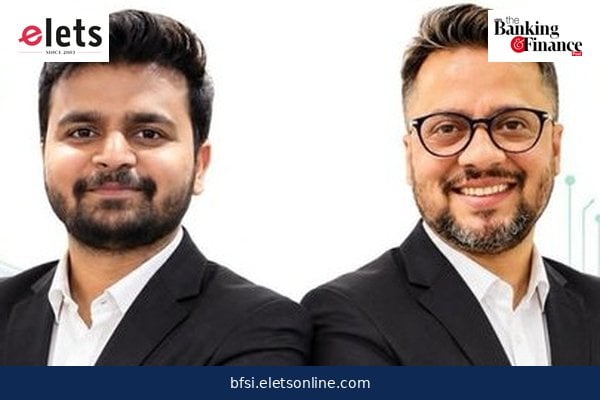
“Most banks we speak to are not short of consent forms. They are short of consent records,” said Abhishek Singh, Co-Founder and CEO, SecureDApp. He added that May 2027 “is not the date to start. It is the date the Board can start asking questions.”
Himanshu Gautam, Co-Founder and CTO, said the hardest engineering problem was keeping consent consistent across a bank’s core banking system, loan origination system, CRMs and partner integrations. SecureCMS treats every consent and withdrawal as an event that each connected system must acknowledge, and logs that acknowledgement.
SecureDApp clarified that SecureCMS is a consent management platform, not a registered Consent Manager under Rule 4 of the DPDP Rules, and is built to work alongside registered Consent Managers. More details are on the SecureDApp website and the MeitY data protection framework page.
Key takeaways
- SecureDApp launched SecureCMS on 2 November 2026 for DPDP consent management in banks and NBFCs.
- DPDP Consent Manager provisions start on 13 November 2026; core consent and breach duties apply from 13 May 2027.
- The platform syncs consent withdrawals to core banking and lending systems while preserving PMLA and KYC retention records.
FAQ
When do DPDP consent rules apply to banks?
Consent Manager provisions take effect on 13 November 2026, and the core notice, consent, security and breach obligations apply from 13 May 2027.
Is SecureCMS a registered Consent Manager?
No. SecureDApp says it is a consent management platform for a bank’s own operations and is designed to work with registered Consent Managers.
Featured image: Himanshu Gautam, Co-Founder and CTO, and Abhishek Singh, Co-Founder and CEO, SecureDApp. Photo: SecureDApp (press release).